 blog
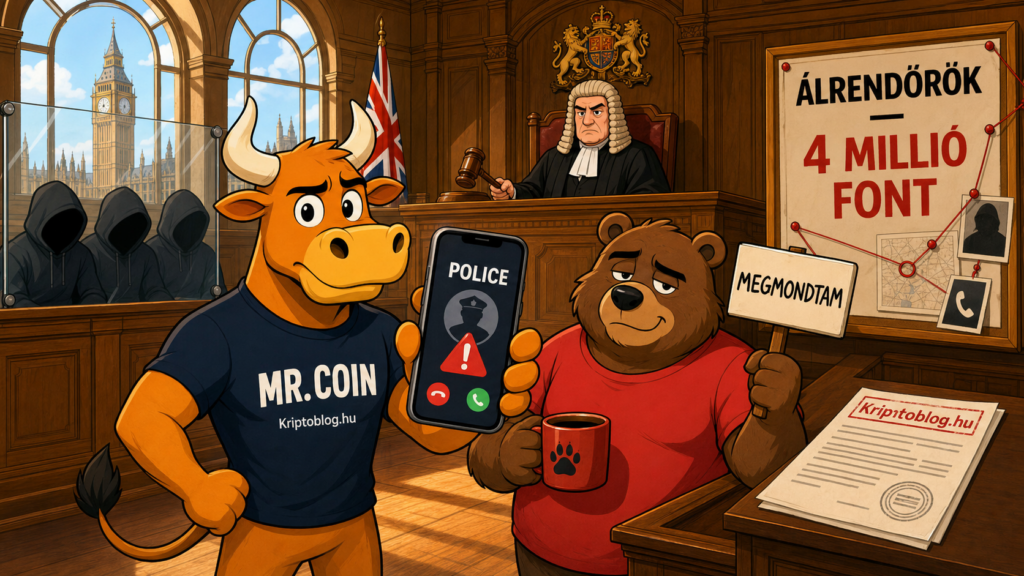
London's Southwark Crown Court has sentenced three men to prison for a crypto fraud built on police impersonation. The group stole more than £4 million in cryptocurrency from eight victims. They did not exploit a protocol flaw — they convinced victims that handing over data or transferring funds was how to protect their wealth.
The Metropolitan Police's July 16, 2026 statement details the sentences and the investigation. Decrypt's follow-up the next day describes the same case as a $5.3 million loss, but gives no reference exchange rate or conversion timestamp. To avoid false precision, this article uses the police's primary figure of more than £4 million throughout. The real takeaway is that the criminals controlled both the danger narrative and the channel used to verify it.
The attackers hijacked the verification process
What the UK case and two documented Hungarian incidents share is not simply urgency. In all three, the same party controlled the entire verification loop: they named the threat, claimed authority to act, supplied the channel that appeared to confirm their story, and then dictated the "safe" solution.
The UK fraudsters posed as police officers and told victims their crypto holdings were at risk. In a Hungarian case in Szekszárd, the caller claimed to work for the Budapest Metropolitan Police Headquarters. In a separate Hungarian case from Szerencs, the caller claimed to be a staff member at a crypto trading platform and cited an unauthorized login. The assumed role made an outsider's instructions look like official assistance, and the danger story reframed data disclosure or a wire transfer as asset protection.
The second layer of deception was cutting off outside verification. The UK group built fake police websites. In the Szekszárd case, a second "policewoman" sent a confidentiality agreement and even instructed the victim not to tell the bank teller the real reason for the transfer. The call and the seeming confirmation both belonged to the same fraud infrastructure, so neither one actually verified the other.
The sources do not say exactly which claim each victim accepted and why. But there is independent research on the role of authority. In two experiments by Maxim Baryshevtsev and Joseph McGlynn, elements leaning on authority and sympathy increased susceptibility to phishing messages. Layered fear and urgency cues, by contrast, reduced susceptibility because they made the fraud attempt easier to spot.
The 2020 study examined emails, not phone-based police impersonation, so its result cannot be mapped directly onto this case. But it does warn that the "urgency always works" explanation is too simple. In the UK case, the authority-projecting role was paired with a fake verification site and a solution dictated by the fraudster. It was not a single psychological lever but mutually reinforcing channels that shut down verification.
The UK government's fraud policy material describes this method as a multi-stage, multi-channel social engineering process. According to the document, criminals impersonate trusted organizations by phone or on fake websites, then generate fear and urgency. From the three cases examined here comes a practical test: if the description of the threat, the route for verifying it, and the requested solution all come from the same inbound contact, no independent verification has taken place yet.
Eight victims, three convictions
According to the Metropolitan Police, Anthony Ikenwe and Kevin Nwamma each received six years for conspiracy to commit fraud and five years for money laundering. Hamza Bashir was sentenced to three years and nine months, plus three years. In all three cases the two sentences run concurrently, so Ikenwe and Nwamma serve six years in practice and Bashir three years and nine months; the terms are not added together.
Ikenwe and Nwamma pleaded guilty in April. Bashir changed his plea on the eighth day of the trial, after the evidence had been presented. The court phase is closed, but the search for the wider network and the stolen assets is not: UK police continue to work with domestic and international partners to identify further participants.
Authorities have so far recovered approximately £1 million in assets directly linked to victims. That is significant, but only a fraction of the losses exceeding £4 million. The case therefore shows two separate outcomes: identifying the perpetrators can succeed even when the full stolen sum is not immediately returned.
No single blockchain trail cracked the case
Victims filed reports in January 2025. Investigators then combined several data streams: blockchain transactions, communications and financial records, crypto exchange data, and internet service provider information. They identified shared aliases, phone numbers, websites, crypto wallets, and spending patterns. Reports that at first appeared unrelated were gradually assembled into a single organized network.
- november 20-án hét londoni és essexi címen hajtottak végre összehangolt intézkedést. Negyven mobiltelefont, további digitális eszközöket, luxuscikkeket és kriptovagyont foglaltak le. A közlemény Kevin Nwammát olyan tárcákból induló utalásokkal is összekapcsolta, amelyek az ő közlekedési vállalkozásához köthető bankszámlákra érkeztek.
The public data also reveals an important technical limit. The Metropolitan Police did not disclose which blockchains the assets moved across, and did not publish wallet addresses, transaction IDs, exchange names, or the analytics software used. Nor did they claim that a mixer was involved. These details cannot be responsibly reconstructed.
The evidence base did not rest on on-chain movement alone. Blockchain data was assessed together with exchange, communications, financial, and ISP information. Seized devices and physical assets were added on top. The statement does not break down the exact evidentiary role of each dataset, but the message is clear: the connection was made by combining different data domains, not by any single source.
The same pattern in two Hungarian cases
In a case reported by Hungary's KiberPajzs cyber-safety program on July 16, 2026, an alleged police approach in Szekszárd ended with 2.47 million forints (roughly $6,900) moved to a "secure account." It was not a crypto case, yet it repeated almost exactly the decision-making architecture of the UK attack: an authority role, a threat narrative, an official-looking document, and then the supposed placing of funds into safety. The KiberPajzs warning is unambiguous: no such thing as a "security account" exists, and neither police nor financial institutions ever ask anyone to protect their money by wiring it to a stranger's account.
A Hungarian National Police statement from August 26, 2025 shows a different entry point. The caller posed as a staff member of a crypto trading platform, cited an unauthorized login, and then persuaded the victim to enter a recovery phrase into a Ledger app. According to the statement, more than $16,000 worth of bitcoin then disappeared; Hungarian police also reported the loss as more than 5 million forints.
The three cases did not ask for the same thing: account credentials or a transfer from the UK victims, a bank wire from the Szekszárd victim, and a recovery phrase from the Hungarian crypto holder. The shared risk was that the caller not only named the problem but also dictated the verification method and the "solution." As long as all three remain in the caller's hands, there is no independent evidence that the danger is real.
Switch to an independent channel
If an inbound call claims your crypto is at risk, the first task is not to verify anything inside that call — it is to change channels. End the conversation, do not initiate any transaction, and do not use the caller's link, phone number, or app suggestion. Then open the service provider's official site or app yourself, or look up the authority's public contact details independently.
After switching channels, three things must be checked separately: whether the reported incident actually exists, whether the organization in question really contacted you, and whether they are permitted to request an action that grants access or moves assets. Two of these being off is enough to stop. Hungarian police state that legitimate financial service providers never ask for a recovery phrase, password, or device identifier by phone; KiberPajzs states that no "secure account" run by police or a bank exists.
If data has already been handed over or a transfer already made, the same rule applies: switch to an official channel. Contact the service provider and the police using details you sourced yourself, not through further discussion with the caller.
The UK verdict does not prove that every crypto movement is easily traceable or that every stolen sum can be recovered. It shows that with off-chain evidence added in, even a complex network can be exposed. For prevention, though, what looks like a technical problem is settled by a communication question: who chose the channel you are using to check whether the danger is real?
Sources
- Metropolitan Police: Men who stole more than £4 million of crypto are jailed, forrás (megtekintve: 2026-07-19)
- Decrypt: Three Men Jailed for Posing as Police in $5.3M UK Crypto Fraud, forrás (megtekintve: 2026-07-19)
- UK Government: Unauthorised fraud in the UK: call for evidence, forrás (megtekintve: 2026-07-19)
- KiberPajzs: „Biztonsági számlás” csalás a rendőrség nevében, forrás (megtekintve: 2026-07-19)
- Magyar Rendőrség: Amikor a mese rémálommá vált, forrás (megtekintve: 2026-07-19)
- Baryshevtsev–McGlynn: Persuasive Appeals Predict Credibility Judgments of Phishing Messages, forrás (megtekintve: 2026-07-19)

Comments
Share your view: questions, corrections, and counterpoints are welcome. Comments are for constructive, useful discussion.